Cloudflare Strict Service Tokens: Migration Guide
Cloudflare's strict service-token authentication mode is now the default—and cannot be disabled—for Zero Trust organisations created on or after 5 October 2026. Existing organisations can choose when to enable it, but Cloudflare recommends that they do.
The setting changes how automated requests are authorised. A machine caller must match a Service Auth policy and keep sending its service-token headers on every request. Failed authentication returns an explicit HTTP 401 or 403 instead of an HTTP 302 redirect to a human login page, and Access no longer issues a CF_Authorization cookie after successful service-token authentication.
For a small or medium business, the risk is practical: a scheduled import, webhook processor, monitoring check, deployment pipeline or private API integration can break even though the protected website still works for staff in a browser. The migration goal is to prove every non-human caller works without relying on an Allow policy, login redirect or cached cookie.
Why this Cloudflare change is trending now
Cloudflare announced strict service-token authentication on 2 October 2026 and switched it on permanently for new Zero Trust organisations from 5 October. That makes the behaviour current production reality rather than an optional preview.
The change also exposes a common integration weakness. Older automation may send a service token once, accept the Access application cookie and reuse that cookie until it expires. Other clients may present service-token headers but sit behind a general Allow policy intended for people. Strict mode removes both shortcuts.
The security rationale is sound: a request that claims to be a machine should be evaluated as a machine on every request. The operational challenge is that browser-oriented and service-oriented authentication often grew together over time. A controlled audit separates them before the setting exposes the mismatch in production.
Which business systems may be affected?
Look for any non-human client that reaches an application protected by Cloudflare Access. The business label matters less than the actual request path.
Scheduled jobs
Product, customer, booking, reporting or finance jobs that call a private endpoint on a timer.
Webhooks
CRM, ecommerce, payment, marketing and support platforms posting events into an Access-protected receiver.
CI/CD
Build, deployment and test pipelines that reach preview sites, admin tools or internal APIs.
Monitoring
Synthetic checks and uptime probes that authenticate to protected staging or production journeys.
Backend services
Application-to-application calls between websites, workers, APIs, dashboards and operational platforms.
AI and agents
Automated assistants or coding agents that call a protected tool or private business endpoint without a human login.
What strict service-token authentication changes
| Behaviour | Before strict mode may allow | With strict mode |
|---|---|---|
| Failed authentication | HTTP 302 redirect to an identity-provider login page | HTTP 401 or 403 response |
| Policy action | A configuration may appear to work through an Allow policy | Only Service Auth can authorise the service-token request |
| Existing cookie | A client may reuse a CF_Authorization cookie | The cookie is ignored for a request presenting service-token headers |
| New cookie | Successful authentication may result in a cookie the client reuses | Access does not return a CF_Authorization cookie |
| Later requests | A client may omit the service token after the first response | Every request must keep presenting the service-token headers |
| Failure evidence | Some machine failures are hard to separate from human login behaviour | Recognised expired, disabled, incorrect or unauthorised service tokens can appear in authentication logs |
The token itself does not automatically grant access. It must be selected by a Service Auth policy attached to the relevant Access application. Cloudflare's documented request normally sends CF-Access-Client-Id and CF-Access-Client-Secret; a self-hosted application can also be configured to accept both values in one custom header when a calling SaaS product supports only one.
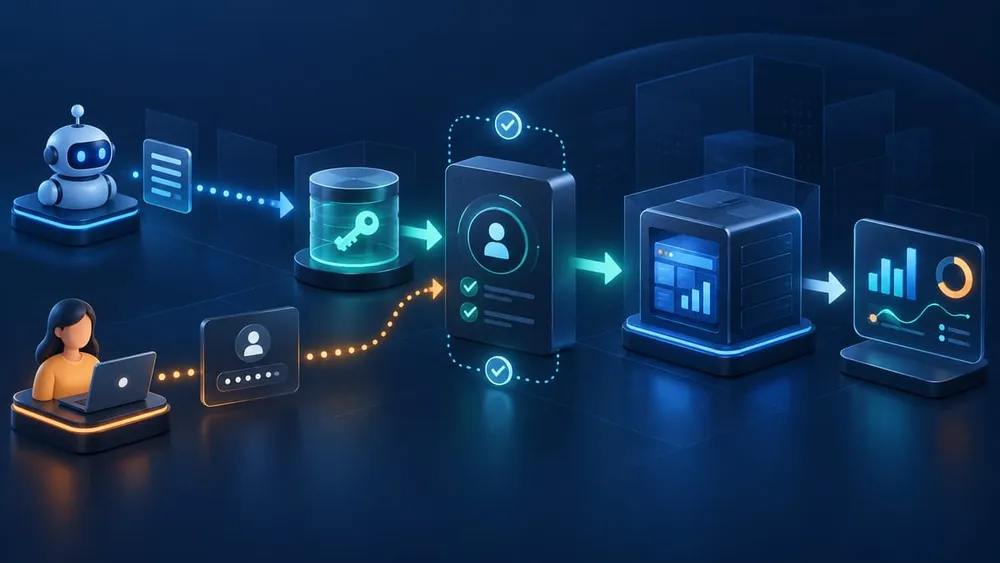
Authenticate every machine request explicitly
Step 1: build a machine-caller register
Start with Cloudflare Access applications, service tokens and policies, then trace outward to the systems that actually use them. Do not assume one token equals one caller: a credential may have been copied into several jobs or environments over time.
For each caller, record:
- business purpose and accountable owner;
- protected hostname, path and Access application;
- service-token name and non-sensitive identifier;
- production, staging, test and development environments;
- where the secret is stored and which workload can read it;
- expected request frequency and critical business outcome;
- current policy action and any extra IP, certificate or network requirements;
- how a failure is detected, alerted and escalated.
Search code, infrastructure configuration, CI variables, secret stores, monitoring tools and vendor settings for the Cloudflare client-header names. Review edge logs and application access logs for calls that never reach the origin. Ask integration vendors whether they send both token values on every request and whether they follow redirects automatically.
If one token is shared across unrelated applications or environments, record the issue rather than trying to clean it up during the same change window. Strict-mode compatibility comes first; separation and rotation can follow through a controlled credential-lifecycle plan.
Step 2: correct the Access policy model
Every machine caller should reach its target through a policy with the Service Auth action. Cloudflare's example includes the intended service token and can require a known IP range as an additional condition.
Review these policy questions before enabling strict mode:
- Is the correct Service Auth policy attached to every relevant Access application?
- Does the policy include only the tokens that need that application?
- Are broad Allow, Bypass or IP rules masking an incomplete machine policy?
- Will an IP-range requirement remain valid for serverless, SaaS or dynamically routed callers?
- Do browser users have a separate identity-based policy rather than sharing a machine path?
- Does the protected path expose more of the application than the automation needs?
Least privilege should be implemented in layers. Scope the service token to the intended Access applications, protect only the routes the integration requires, and constrain the origin credentials or application role behind Access as well. Passing the edge policy should not give an automation administrative rights it does not need.
Keep a rollback path for the setting on older organisations, but do not treat rollback as the final fix. New organisations cannot turn strict mode off, and Cloudflare recommends the stricter behaviour for existing accounts.
Step 3: remove redirect and cookie dependencies
A machine client should treat authentication as an API contract, not as a browser session. Send the service-token credentials on every request, disable automatic redirect following during compatibility tests, and classify 401, 403, 429 and 5xx responses separately.
Why disable redirects in tests? A client that follows an HTTP 302 to a login page may report a final HTTP 200 after downloading HTML. The job can then fail later while parsing the body—or worse, treat a login page as valid data. Strict mode improves this by returning 401 or 403 directly, but tests should prove the client handles those statuses safely.
Remove logic that captures or persists CF_Authorization after service-token authentication. Do not build a replacement cookie cache. The client should retrieve the correct secret from its approved secret store, attach the headers to each request and avoid logging either value.
For a third-party SaaS integration that supports only one custom header, Cloudflare documents an application setting that can accept a JSON credential pair in a single configured header. Confirm the vendor protects that header as a secret and does not expose it in request histories, support exports or error screens.
Step 4: test the failures as carefully as success
Use a non-production Access application with the same policy shape as production. Enable strict mode where it is safe to do so, or test in a new organisation where strict mode is already mandatory. Exercise the actual client rather than only a command-line request.
| Test | Expected result | Evidence to keep |
|---|---|---|
| Valid token and matching Service Auth policy | Protected request succeeds and the intended business action completes | Request ID, timestamp, origin result and business record |
| No service-token headers | Request is denied without creating a partial business action | Status, response shape and application-side absence |
| Incorrect Client Secret | Explicit authentication failure; no unsafe retry storm | 401/403, Access event where available and alert |
| Valid token not included in the app policy | Authorisation failure | Policy decision, application and token identifier |
| Disabled or expired token | Authentication failure visible to operations | Access log event, alert route and runbook link |
| Cookie without token headers | No machine access through a stale service-token session | Denied request and confirmation the client no longer depends on cookies |
| HTTP redirect handling | The client does not accept an identity-provider HTML page as an API success | Final status, content type and parser behaviour |
| Repeated or concurrent requests | Each request authenticates and the business workflow remains idempotent | Request count, duplicate protection and final state |
Test every method and path used in production. A successful health check on GET / does not prove that a webhook can POST to its receiver or that a deployment job can reach a protected admin endpoint.
Six checks before enabling strict mode
Treat the setting as an integration release with security, functional and operational evidence.
Complete inventory
Every machine caller, environment, protected path and business owner is recorded.
Correct policies
Every caller matches a Service Auth policy rather than relying on Allow or a browser login flow.
Per-request headers
The client sends its token on every request and does not capture or reuse an Access cookie.
Safe failures
401, 403, network and origin failures are bounded, visible and cannot create duplicate actions.
Useful telemetry
Access, edge, origin and business signals can be correlated with a request or Ray ID.
Owned rollback
An older organisation has a time-limited rollback decision, named approver and permanent remediation plan.
Monitor authentication and the business outcome
Cloudflare says strict mode records recognised failures for expired or disabled tokens, incorrect Client Secrets and tokens not authorised for the application. It does not log malformed headers or unknown Client IDs. That boundary matters: an empty Access log does not prove the client sent a valid request.
Combine four evidence layers:
- Client telemetry: outbound request count, final status, timeout, retry count and a non-sensitive correlation ID.
- Cloudflare evidence: Access policy decision, authentication event where supported, Ray ID and edge response.
- Origin telemetry: request received, application authentication, processing result and latency.
- Business evidence: order imported, lead created, report refreshed, deployment completed or monitoring journey passed.
Authentication logs and per-request logs serve different purposes. Cloudflare notes that an authentication event does not capture every action inside a session. For strict service-token calls, design alerts around the complete request path instead of assuming one dashboard is exhaustive.
Useful post-change alerts include sustained 401 or 403 rates by application, callers that stop sending expected traffic, unusual request volume, repeated invalid-secret failures, origin errors after successful Access authentication and business workflows that fall behind.
Use the migration to improve credential ownership
Strict mode fixes authentication semantics, but the service token remains a static credential pair. Store it in a central secret-management system, limit runtime access, keep it out of repositories and logs, and use separate credentials for unrelated applications and environments.
ASD's September 2026 guidance recommends short-lived dynamically issued credentials for applications and workloads where possible. When static credentials are required, it recommends central secret management and unique credentials across applications, workloads and development, test, staging and production environments.
Cloudflare service tokens have an explicit duration. Record expiry ownership and alerts. When rotating a Client Secret, Cloudflare supports a grace period from one hour to 30 days during which both the old and new secret can work. Use that window to deploy the new secret, verify every caller, then allow the old value to expire. Do not leave both values active indefinitely.
If a token may be compromised, shorten the plan: rotate or revoke it, update the intended callers, review Access and origin evidence, and confirm the credential was not shared across unknown workloads. A shared token turns one incident into a discovery project.
A seven-day migration plan for an existing organisation
Day 1: confirm the setting and owners
Record the Zero Trust organisation creation era, current strict-mode state, Access administrators and business owner for each protected application.
Day 2: inventory callers and policies
Map service tokens to applications, environments, workloads, secret stores and expected business outcomes. Find callers that rely on Allow policies or unknown shared credentials.
Day 3: fix one representative integration
Create or correct its Service Auth policy, send headers on every request, remove cookie handling and verify explicit failure behaviour.
Day 4: run the test matrix
Test valid, missing, incorrect, disabled and unauthorised credentials, redirect behaviour, retries and the complete business action.
Day 5: prepare telemetry and support
Connect client, Cloudflare, origin and business signals. Give support a symptom list, escalation contact and safe evidence checklist.
Day 6: enable during a controlled window
Use a named approver, low-risk timing and active monitoring. Validate the highest-value integrations first and keep the rollback decision explicit for older organisations.
Day 7: close gaps and schedule lifecycle work
Resolve missed callers, separate shared credentials, set expiry alerts, plan rotation and archive the compatibility evidence with the integration register.
Questions to ask your developer or support partner
- Which Cloudflare Access applications receive machine-to-machine traffic?
- Can you show the caller, service token, policy action and protected path for each integration?
- Does every caller send both service-token values on every request?
- Does any client follow a 302 redirect or reuse
CF_Authorization? - Which tests prove 401 and 403 responses are handled without partial or duplicate work?
- Can Access, edge, origin and business events be correlated during an incident?
- Where are the secrets stored, who can read them and when do they expire?
- What is the rollback decision for an older organisation, and when will the permanent fix be complete?
A credible answer includes an inventory, policy evidence, test results and named ownership. A screenshot showing that one token exists is not enough.
This change also pairs well with VaniTech's inactive API token cleanup guide and Cloudflare Workers observability guide. Strict authentication, credential lifecycle and end-to-end monitoring solve different parts of the same operational risk.