Drupal AI Security Update: September 2026 Patch Guide
Patch Drupal AI and AI Translate vulnerabilities safely with affected-version guidance, permission tests, chatbot checks and a practical rollout plan.
Drupal released three coordinated security advisories for its AI ecosystem on 2 September 2026. Two affect AI-assisted translation permissions. The third covers a cross-site scripting path in an uncommon legacy chatbot setup where prompt injection can reach structured output.
The advisories are rated moderately critical, not critical or highly critical. That distinction matters, but it is not a reason to ignore them. Drupal's main AI project reports 17,818 installations and supports chatbots, content assistance, automation, search and many model providers. A business website may use only one small part of that stack, yet still carry an affected package or submodule.
This guide is for Australian Drupal owners, digital teams, developers, operations managers and technology decision-makers. It explains who is affected, which fixed versions to target, what to test and how to prove the update worked.
Three vulnerabilities, two upgrade paths
First identify whether translation comes from the main AI package or the standalone AI Translate project.
CVE-2026-84911
Cross-site scripting in legacy AI Chatbot structured results. Fixed in AI 1.3.13 and 1.4.8.
CVE-2026-84912
Access bypass in the AI package's AI Translate submodule. Fixed in AI 1.3.13 and 1.4.8.
CVE-2026-84913
Access bypass in standalone AI Translate. Fixed in AI Translate 1.3.2 and 1.4.1.
Check whether your Drupal site is affected
Do not decide from the visible feature name alone. AI Translate was part of the main AI project until AI 1.4.0, when it moved into a standalone contributed project. Two sites with the same "Translate using AI" button can therefore need different package updates.
| Installed project | Affected versions | Fixed version | Main check |
|---|---|---|---|
drupal/ai 1.3.x | Below 1.3.13 | 1.3.13 or later in the branch | AI Translate submodule and legacy chatbot setup |
drupal/ai 1.4.x | 1.4.0 to 1.4.7 | 1.4.8 or later in the branch | AI Translate submodule and legacy chatbot setup |
drupal/ai_translate 1.3.x | Below 1.3.2 | 1.3.2 or later in the branch | Standalone translation permissions |
drupal/ai_translate 1.4.x | 1.4.0 | 1.4.1 or later in the branch | Standalone translation permissions |
Inspect composer.lock, not only composer.json. The lock file records what production should actually install. Confirm the deployed version too; a merged lock-file change does not prove the production release completed.
Also check whether the relevant submodules are enabled, which roles can invoke AI translation, whether translated entities reference restricted fields or entities, and whether a public or editorial chatbot still uses a legacy structured-results configuration.
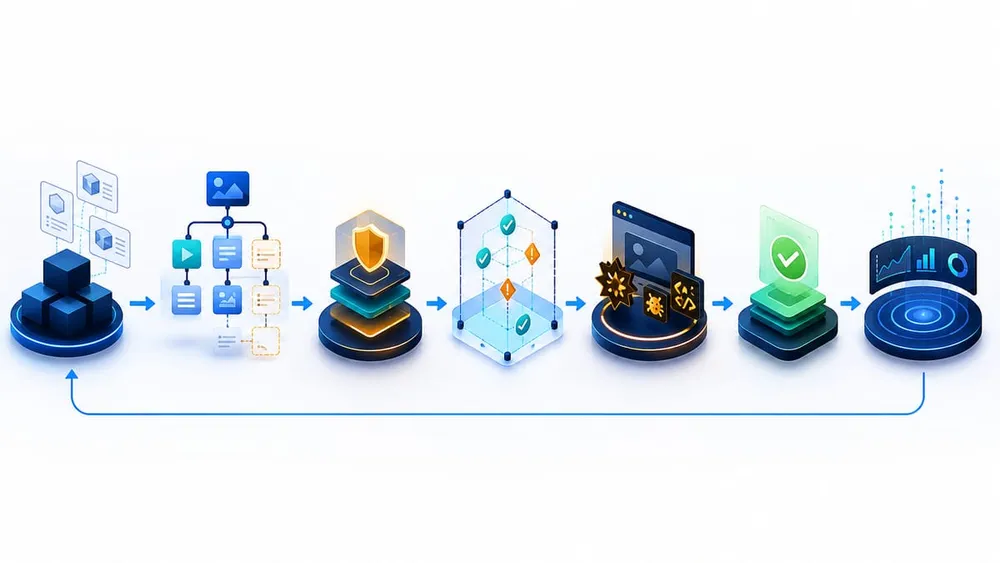
Trace the whole AI path, not only the package
Why these AI vulnerabilities need feature-level testing
Translation access bypass
The two translation advisories describe the same business problem across different package arrangements: during AI translation, the module did not sufficiently check access to the target entity, related fields or referenced entities where those permissions differed from the parent entity.
Drupal says the bypass is limited to the translation operation and does not grant general read or update access. Even so, a translation workflow can process content a user should not be able to translate. That matters for unpublished material, internal notes, embargoed content, restricted product data and referenced records with a different access policy.
Chatbot output and prompt injection
The chatbot advisory is narrower. It affects structured results in an uncommon setup created with AI 1.0.x and AI Agents 1.0.x. Exploitation requires prompt injection placed in editorial content and a path that invokes it. Configurations created or updated after those older branches are not affected according to Drupal.
That mitigation should shape the test plan, not replace the patch. If the site exposes an AI assistant, identify its content sources, confirm the agent configuration lineage and test how structured output is rendered. Treat model output as untrusted input at the browser boundary.
Build a fast Drupal AI exposure inventory
A useful inventory connects software versions to business features and owners. Capture the following before changing code:
| Area | Evidence to collect | Why it matters |
|---|---|---|
| Packages | Installed drupal/ai and drupal/ai_translate versions from Composer | Determines the required fixed branch |
| Enabled modules | AI Chatbot, AI Translate and related agent modules enabled per environment | A package can be present without the vulnerable feature being active |
| Roles and permissions | Roles allowed to translate, edit source content, administer AI or invoke chatbots | Defines who can reach each code path |
| Content model | Restricted fields, references, unpublished content and translation settings | Reveals meaningful permission boundaries |
| Agent configuration | Creation history, structured-result templates and content sources | Identifies the legacy XSS condition |
| Public surfaces | Chat widgets, APIs, forms and pages that invoke AI functionality | Shows exposure and customer impact |
| Operations | Technical owner, deployment route, rollback, logs and alerts | Prevents an unowned patch or silent failure |
If the original implementation team is unavailable, treat this as a technical takeover exercise. Establish the repository, hosting access, deployment process, backups and monitoring before making an emergency production-only edit.
Patch Drupal AI in a controlled release
- Confirm the affected branch. Use Composer and deployed-environment evidence to identify the package and exact version.
- Read the advisory and release notes. Keep the update within the current minor branch unless a separate upgrade has been assessed.
- Back up code, files and the database. Verify that restoration is practical, not merely that a backup job exists.
- Preview dependency changes. Run the relevant Composer update with
--dry-runand review every proposed package change. - Update the specific project. For the main package, target the safe 1.3 or 1.4 branch. For standalone translation, target its safe branch. Allow required dependencies without turning the security response into an uncontrolled whole-site upgrade.
- Run database updates and rebuild caches. Follow current Drupal guidance, then export and review any configuration changes.
- Execute regression and security tests. Cover ordinary editing, translation, restricted references, chatbot rendering and provider calls.
- Deploy through the normal release path. Preserve the reviewed lock file, change record and rollback point.
- Verify production. Confirm the deployed package version, feature behaviour, logs and monitoring after release.
Typical commands include composer audit, a targeted composer update drupal/ai --with-all-dependencies or composer update drupal/ai_translate --with-all-dependencies, followed by drush updatedb, drush cache:rebuild and drush config:export --diff. Adjust constraints and commands to the repository's existing workflow rather than copying them blindly into production.
Use a test matrix that matches the advisories
| Scenario | Expected result after patch | Evidence |
|---|---|---|
| Author translates content they can edit | Translation succeeds and expected fields update | Role, entity ID and before/after state |
| User cannot access a restricted referenced entity | Translation cannot use the restricted data | Denied path and unchanged restricted entity |
| User can edit the parent but not a protected field | Protected field remains inaccessible and unchanged | Permission configuration and saved entity state |
| Translation of unpublished or embargoed content | Existing access policy remains enforced | Publication state and role-specific result |
| Normal chatbot question | Answer renders without script-capable markup | Rendered DOM and browser console |
| Hostile instructions embedded in indexed editorial content | Content cannot create executable output in the user's browser | Test fixture, response and rendered DOM |
| AI provider unavailable or rate-limited | Workflow fails safely without partial or unauthorised content changes | Application logs and entity state |
| Cache rebuild and scheduled jobs | Queues, cron and normal publishing remain healthy | Status report, logs and smoke tests |
Use dedicated test content and non-production provider credentials where practical. Do not test exploit strings against live customer content or expose sensitive prompts and model responses in screenshots or shared tickets.
If you cannot patch immediately
The preferred response is to install the fixed version. If a dependency conflict or failed regression test delays the release, reduce exposure while the repair is completed:
- disable the affected AI translation or chatbot feature if the business can operate without it
- remove permissions from roles that do not need AI translation
- restrict access to editorial AI tools to trusted staff
- remove or rebuild legacy agent configurations linked to structured results
- limit public chatbot content sources and monitor unusual responses
- record the exception, owner, expiry date and planned patch window
These are temporary controls, not substitutes for the vendor fix. Australian Cyber Security Centre guidance recommends patching according to exposure, assigning clear responsibility and confirming that updates were applied successfully. Its current guidance for medium-sized businesses also calls for rapid patching and minimum privileges on internet-facing services.
Turn the advisory into verified business protection
The goal is not simply a new package number. It is a tested, owned and observable AI feature.
Day 1: inventory
Confirm packages, versions, enabled features, permissions, owners and exposed surfaces.
Days 1-2: patch
Update the correct branch in a controlled environment and review dependency changes.
Days 2-4: test
Exercise normal workflows, denied permissions, hostile content and failure paths.
Days 4-7: release
Deploy, verify the production version, monitor errors and close the evidence record.
Keep Drupal AI security maintainable
This advisory set exposes a broader operational lesson: AI features cross several trust boundaries at once. Editorial content becomes model input. Model output returns to a CMS or browser. Translation can touch fields and references with different access rules. External providers add credentials, network calls and data-handling decisions.
Assign an owner for the complete feature, not just the module. Maintain an inventory of AI packages and providers, subscribe to Drupal security notices, run dependency audits in CI, review permissions after role changes, retain useful application logs and test rollback. For public chatbots, monitor rendering errors, unusual response patterns and provider failures without storing unnecessary sensitive content.
When adding a new AI use case, include security acceptance criteria before release: approved content sources, allowed roles, output handling, provider data policy, failure behaviour, audit evidence and a named maintenance owner. That is how a quick experiment becomes a dependable business capability.
Sources Checked
- Drupal Security Team: SA-CONTRIB-2026-119
- Drupal Security Team: SA-CONTRIB-2026-120
- Drupal Security Team: SA-CONTRIB-2026-121
- Drupal.org: AI project
- Drupal.org: AI Translate project
- Drupal.org: updating modules and themes with Composer
- Drupal Security Team: security risk levels
- ASD's ACSC: patching applications and operating systems
- ASD's ACSC: defending against AI-enabled cyber attacks