Critical Drupal Security Release: 14 October Patch Plan
The Drupal Security Team will publish a critical core security release for all supported branches on 14 October 2026 between 16:00 and 21:00 UTC. The pre-announced vulnerability is rated 19 out of 25, at the top of Drupal's Critical range, and the team warns that exploits could be developed within hours or days.
For organisations in Sydney and Melbourne, the release window is 03:00 to 08:00 AEDT on 15 October. That makes this an ownership and readiness problem as much as a technical one. Someone needs to watch the final advisory, identify the correct fixed version, build and test the update, deploy it safely and confirm that customer-facing journeys still work.
This guide is for Australian business owners, operations managers, digital teams and technology decision-makers responsible for Drupal websites, portals or integrations. It explains what is known now, what must wait for the final advisory and how to run a controlled same-day response.
Why this Drupal update is trending now
Drupal published the advance security announcement on 12 October so site owners could reserve an update window. Unlike a routine maintenance release, this one is explicitly rated Critical and applies to all supported core branches.
The notice deliberately withholds vulnerability details until fixed releases are ready. That is normal responsible-disclosure practice. Do not infer the affected feature, attack path or exploitability of a particular site from speculation online. The authoritative facts will be the final Drupal advisory and release notes.
The commercially useful response is to shorten the safe path from disclosure to verified production deployment. That means preparing the estate, people, backups, test environment and release process before the fixed packages appear.
Three facts to plan around
Drupal's pre-announced risk score, classified as Critical.
19/25
The announced 16:00-21:00 UTC security release window.
5 hours
ASD's target for critical vulnerabilities in online services.
48 hours
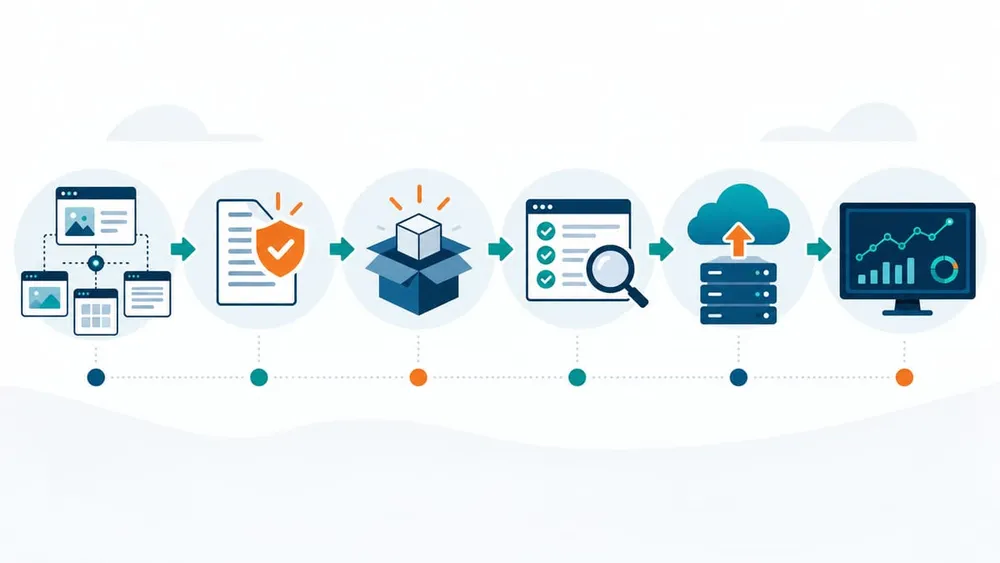
Move from advisory to verified production safely
What to do before the fixed release is published
- Name an incident owner and deployment owner. Decide who will read the advisory, who can approve the release, who can deploy and who will verify business functions.
- Inventory every Drupal instance. Include public websites, customer portals, campaign sites, intranets exposed through remote access, staging copies and disaster-recovery environments. Record the core branch, current patch version, hosting location, repository, deployment method and support contact.
- Move to the latest supported patch if practical. Drupal recommends resolving ordinary update blockers before the security window. Do this only through your established test and deployment process.
- Prove the backup is usable. Confirm database, uploaded files, code, configuration and secrets can be restored to a consistent point. A backup job that has never been restored is not release insurance.
- Prepare a production-shaped test environment. Refresh enough content and configuration to exercise authentication, forms, search, cache, integrations and scheduled jobs without exposing live personal information.
- Freeze unrelated changes. Keep the security update small. Mixing feature work into an urgent patch makes failures harder to diagnose and rollback harder to trust.
- Set the watch window. Subscribe to Drupal security updates and make sure the overnight hand-off is explicit for Australian teams.
An Australian overnight runbook
| When | Owner | Required outcome |
|---|---|---|
| Before 03:00 AEDT | Service owner | Estate, contacts, backup evidence, test environment and maintenance window are ready. |
| From 03:00 AEDT | Technical lead | Watch Drupal's official advisory and release index; record affected branches, fixed versions, mitigations and special instructions. |
| After fixed packages appear | Developer or support provider | Update the dependency set in a controlled environment and retain the changed lock file and build evidence. |
| Before production | Tester and business owner | Run technical checks plus priority customer journeys; document the release decision and rollback trigger. |
| Deployment window | Release owner | Deploy the tested build, apply database updates if required, rebuild caches and verify the running version. |
| After release | Operations owner | Monitor logs, availability, forms, transactions and integrations; escalate suspicious activity or failed verification. |
The times above are a planning conversion from the announced UTC window, not a promise that every fixed package will appear at 03:00. Use the official advisory as the release trigger.
Supported does not mean equally future-ready
Check the final advisory for exact fixed versions. These branch decisions shape the work around the patch.
Drupal 11.4.x
The current Drupal 11 minor branch is in the security release schedule. Patch to the version named by the final advisory and keep the normal regression suite.
Drupal 11.3.x
It remains in the current security window but support ends in December 2026. Apply the security fix and keep the move to a supported minor branch on the roadmap.
Drupal 10.6.x
It is covered now but Drupal 10 reaches end of life on 9 December 2026. Treat the patch as urgent maintenance, not a replacement for the Drupal 11 upgrade plan.
Older Drupal branches
Do not assume a normal official patch will exist. Isolate exposure, seek qualified support and create a supported-version migration plan immediately.
Managed hosting
Ask whether the provider patches code automatically, only offers a platform mitigation, or expects your team to deploy. Request the exact version and evidence.
Drupal Steward
It may protect against some known attack vectors, but Drupal says it will not cover every possible exploit. Keep the core update in scope.
Use the advisory, not a guessed version number
At the time this article was prepared, the fixed packages and full vulnerability details had not been published. The Drupal core release index and the final security advisory are the authoritative sources.
Record four things before changing production:
- the affected core branches and configurations
- the exact fixed version for your branch
- any dependency, configuration or mitigation instructions
- whether there are known regressions or follow-up releases
A social post, hosting banner or package-manager notification can alert you, but it should not replace the official release notes. If your current branch is unsupported, do not force a package intended for another branch into production. Use isolation or a vendor-supported mitigation while planning the required upgrade.
A controlled Composer update path
Most modern Drupal projects should update core through Composer. The exact command depends on how the repository declares Drupal, so inspect composer.json and the official release notes before running anything.
- Create a release branch from the deployed commit. Do not patch from an unverified developer workstation state.
- Capture the before state. Record the deployed commit, Drupal version, PHP version, database version and current status report.
- Resolve the official fixed dependency set. Drupal's common pattern for
drupal/core-recommendedprojects is to updatedrupal/core-*with dependencies, but the release advisory takes precedence. - Review the diff. Check
composer.json,composer.lock, patches, scaffolding files and unexpected transitive dependency changes. - Build a clean artifact. Run automated tests, static checks and a dependency install from the lock file so production receives the same tested versions.
- Apply Drupal update steps. Run required database updates, rebuild caches and review the status report in the test environment.
- Promote the tested artifact. On production, install the locked dependency set rather than calculating a fresh one. Preserve logs and deployment evidence.
The official Composer guide notes that package output and Drupal's status report can disagree after a failed update. Verification must check the running application, not only a successful command exit.
Test the business website, not only Drupal core
A security patch is incomplete until the business service works and the running version is proven. Build a short test matrix around the journeys that create revenue, enquiries or operational work.
| Area | Minimum verification |
|---|---|
| Version and health | Expected Drupal version, clean status report, successful database updates, rebuilt caches and no new critical log entries. |
| Anonymous experience | Homepage, navigation, search, high-traffic landing pages, redirects and cached pages work without an authenticated session. |
| Content operations | Editor login, content edit, media upload, preview, workflow and publication work for the roles that use them. |
| Forms and transactions | Critical forms submit once, validation works, notifications arrive and CRM, payment, booking or helpdesk records are created correctly. |
| Integrations | API authentication, webhooks, scheduled jobs, queues, search indexing and downstream synchronisation complete without duplicate work. |
| Performance and security edge | CDN, WAF, cache, headers, uptime checks and error rates remain within the normal baseline. |
Define the rollback trigger before deployment. A rollback should restore a consistent code, database and file state; replacing code alone may not be safe after a database update.
If you see suspicious activity, patching is not enough
A patch closes a known vulnerability; it does not remove an attacker who may already have gained access. If logs, file integrity checks, new administrator accounts, unusual jobs or outbound traffic suggest compromise, move from routine maintenance to the organisation's incident-response process.
- preserve relevant application, web server, identity, hosting, CDN and WAF logs
- record the timeline and avoid destroying evidence through ad-hoc cleanup
- contain affected systems using a qualified incident responder
- rotate exposed credentials and secrets through a planned sequence
- review persistence mechanisms, changed files, database content and privileged accounts
- assess privacy, contractual and regulatory notification obligations
- restore only from a trusted point and monitor closely after recovery
Do not assume the absence of an obvious homepage change means the site is clean. Modern intrusions may target customer data, administrator sessions, payment flows or future access rather than visible defacement.
Questions to ask your Drupal support provider
- Which of our production and non-production sites are affected?
- What core branch and exact patch version is each site running now?
- Who is monitoring the release window and what is the expected response time?
- Will you deploy a tested core update, a temporary mitigation or both?
- Which backups have been verified, and what is the rollback boundary?
- Which customer journeys and integrations will be tested?
- How will you prove the running production version after deployment?
- What logs and alerts will be monitored for attempted exploitation or regression?
- If our branch is near or beyond end of support, what is the funded upgrade plan?
A useful answer includes owners, timestamps, evidence and a clear exception path. “The host handles security” is too vague for a critical CMS release.
A practical priority for small and medium businesses
SMEs do not need an enterprise change board to handle this well. They do need one accountable owner, an accurate site inventory, a tested backup, access to the code and hosting accounts, a staging environment or reproducible local build, a short business test list and a provider who can act inside the required window.
If those basics are missing, this release is also a technical-takeover warning. Recover repository access, hosting ownership, domain and CDN control, deployment documentation and named support responsibilities now. The next security notice should not begin with a search for credentials or the person who last touched the site.
The immediate outcome is a verified patch. The longer-term outcome is a maintainable Drupal estate with supported versions, repeatable releases, monitored customer journeys and evidence that recovery works.
Questions site owners are asking
Sources Checked
- Drupal Security Team: Upcoming critical Drupal core release on October 14, 2026
- Drupal Security Team: Security risk levels defined
- Drupal.org: Updating Drupal core via Composer
- Drupal.org: Deploying a Drupal update
- Drupal.org: Drupal core release schedule
- Drupal.org: Releases for Drupal core
- Australian Signals Directorate: Patching applications and operating systems
- Australian Signals Directorate: Essential Eight maturity model