Drupal Security Advisories: A 2026 Response Plan
Respond to Drupal's 2026 security advisory surge with an exposure-based plan for inventory, triage, patching, testing and ongoing maintenance.
The Drupal Association reported 256 security advisories from June through October 2026—more than the 250 advisories published across the previous 30 months combined. October produced 106 advisories, including a record 39 on 28 October.
Those numbers deserve attention, but not panic. Drupal says the surge reflects cheaper AI-assisted discovery of latent issues and a larger disclosure pipeline, not a sudden expansion of Drupal's underlying attack surface. Every advisory still needs to be checked against the projects, versions, configuration and permissions on your own website.
The commercial lesson is clear: occasional manual patching is no longer a reliable operating model. Businesses need an inventory, a repeatable triage rule, a controlled release path and evidence that the live site is actually protected.
VaniTech supports CMS development, ongoing website maintenance and technical takeover of business-critical websites.
The Security Signal Changed in 2026
Drupal's published data shows a step change in discovery and disclosure volume.
256 Advisories
Published between June and October 2026.
106 in October
The highest monthly total reported in the initiative results.
39 in One Day
A record publication batch on 28 October.
134 Reporters
Credited since 1 June, versus 68 during all of 2025.
Why Drupal security advisories are trending now
AI-assisted analysis has made it much cheaper to scan mature open-source code for vulnerability patterns. Drupal's Security Engineer in Residence initiative says this changed where the bottleneck sits: finding possible issues became fast, while human intake, duplicate detection, validation, fixing, review and release capacity became the constrained parts of the process.
That matters beyond Drupal. The initiative reports that similar automated-disclosure growth is appearing across major open-source ecosystems. A website owner should therefore expect more security signals across CMS packages, PHP libraries, JavaScript dependencies and connected services—not fewer.
Higher visibility can be a positive sign when reports are responsibly validated, fixed and published. The risk to a business comes from having no dependable way to match that growing stream against what is actually installed and exposed.
Do not treat every advisory as equal
Drupal advisories include a 0–25 risk score built from six factors: access complexity, authentication required, confidentiality impact, integrity impact, exploit availability and target distribution. Scores from 15 to 19 are labelled Critical; lower scores can still matter when an exposed feature handles sensitive data or sits on an important customer journey.
The published severity is a starting point, not your final priority. Your decision should also consider:
- Whether the affected module, theme, core version or dependency is installed.
- Whether the vulnerable submodule or feature is enabled.
- Whether the affected route or capability is reachable from the internet.
- Which roles can access it and whether those permissions are broader than intended.
- Whether the site stores customer, member, payment, health or other sensitive information.
- Whether public exploit code or active exploitation evidence exists.
- Whether a supported fixed release, configuration mitigation or replacement project is available.
A large advisory batch should trigger a structured comparison, not 39 uncoordinated emergency changes.
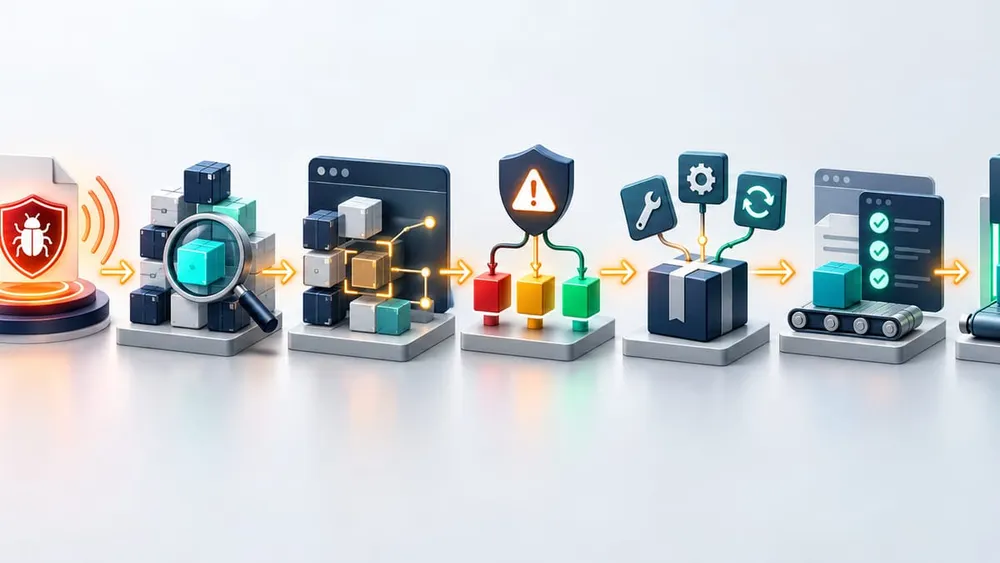
An eight-step Drupal advisory response plan
- Freeze the evidence. Record the advisory URL, publication time, affected versions, fixed releases, configuration conditions and current site state.
- Match the inventory. Compare the advisory with the deployed core version, Composer lock file, enabled extensions, themes, custom modules and hosting stack.
- Confirm exposure. Check whether the affected functionality, route, permission, data flow or integration is active on this website.
- Assign business priority. Combine Drupal's risk rating with exploit evidence, internet exposure, data sensitivity, operational criticality and available mitigations.
- Choose a response. Update, disable, uninstall, replace, reconfigure or temporarily restrict access. Record why the chosen action is sufficient.
- Build and test away from production. Update dependencies in a controlled environment, commit the lock file, run database updates and exercise the affected business journeys.
- Deploy and verify. Use the tested lock file in production, run required database and cache steps, confirm the live versions and repeat high-risk checks.
- Monitor and close. Review logs, error rates and security alerts, preserve evidence, then track any temporary mitigation until it is removed.
This sequence lets a team process a batch consistently. It also leaves an audit trail for business owners, insurers, auditors, clients and future maintainers.
Use a simple exposure and priority matrix
| Finding | Typical priority | Practical response |
|---|---|---|
| Affected package is not installed | Record and close | Keep inventory evidence showing why the site is not affected. |
| Installed but vulnerable feature is disabled and unreachable | Planned with verification | Confirm the mitigation, restrict access where possible and schedule the supported update. |
| Internet-facing feature on an affected version | Urgent | Apply the vendor fix or documented mitigation through an accelerated tested release. |
| Known exploit or authentication bypass affecting a live journey | Emergency | Restrict exposure, patch rapidly, preserve logs and check for indicators of compromise. |
| Project is unsupported for security reasons | Urgent architectural decision | Remove, replace or fund a supported remediation path; do not treat silence as safety. |
| Custom module resembles the vulnerable pattern | Targeted review | Review the custom code, add a regression test and deploy a fix through normal controls. |
The matrix should be adapted to the organisation's risk appetite, contractual commitments and data. A public brochure site and a member portal can run the same module but face very different consequences.
Build an inventory that can answer the question quickly
An advisory cannot be triaged reliably from the Drupal admin screen alone. Keep a current technical inventory containing:
- Drupal core branch and exact deployed version.
- Composer-managed package names and locked versions.
- Enabled and installed contributed modules, submodules and themes.
- Custom modules, patches and forks with named owners.
- Projects not covered by Drupal's security advisory policy.
- Unsupported or abandoned packages and their replacement plans.
- Public routes, forms, file uploads, APIs, webhooks and authenticated areas.
- Hosting, PHP, database, search, storage and reverse-proxy dependencies.
- Business owner, technical owner, maintenance provider and escalation contacts.
Drupal's Update Status module can periodically check core, modules and themes, while composer audit can identify advisories across the locked PHP dependency tree. Use both as inputs. Neither replaces a site-specific inventory, configuration review or test plan.
Security coverage also matters. Contributed-project maintainers opt into Drupal Security Team coverage. A package without coverage may have no coordinated advisory even when a problem exists, so coverage status belongs in procurement and maintenance decisions.
Patch through a controlled Composer workflow
Drupal's current guidance uses Composer for core and contributed projects. The safe pattern is to change dependencies in development or staging, review the result, commit the updated composer.lock, and deploy that tested lock file to production with composer install --no-dev. Do not improvise a different dependency resolution directly on the live server.
Minimum release evidence
- Pre-change database and file backup, plus a tested restoration path.
- Before-and-after package versions and Composer audit result.
- Release notes and advisory conditions reviewed.
- Database updates and cache rebuild completed successfully.
- Drupal Status report checked before and after the change.
- Automated checks, manual journey tests and accessibility checks recorded.
- Production version, deployment time and operator confirmed.
- Rollback trigger and responsible decision-maker named.
Australian cyber guidance recommends rapid patching for internet-facing services and prompt review of their logs. Speed and control are compatible when the team has rehearsed the release path before the emergency arrives.
Test business journeys, not only the homepage
| Area | Checks after a security update |
|---|---|
| Public content | Key pages, navigation, search, media, redirects, metadata and cache behaviour. |
| Forms and leads | Validation, CAPTCHA, file uploads, confirmation messages, email delivery and CRM handoff. |
| Accounts and permissions | Login, logout, password reset, SSO, role boundaries and administrative access. |
| Content operations | Create, edit, preview, moderate, schedule, publish, translate and roll back content. |
| Commerce or transactions | Catalogue, cart, checkout, payment callback, order status, customer email and refund flow. |
| Integrations | APIs, webhooks, queues, cron, search indexing, analytics and third-party authentication. |
| Operations | Error logs, security alerts, performance, cache hit rates, scheduled jobs and backup completion. |
Start with the journey the advisory can affect, then run a compact regression set across the rest of the site. A technically successful dependency update is not complete if a customer form stops reaching the CRM or an editor can no longer publish.
Have a plan for unsupported and unmaintained projects
Some advisories mark a contributed project unsupported because a known security issue has not been fixed. That is not a normal patch ticket. It is a product and architecture decision.
The immediate options are usually to disable or uninstall the project, replace it with a supported alternative, restrict the affected functionality while a migration is built, or fund a properly reviewed remediation and maintenance path. The right choice depends on how deeply the project is embedded in content, configuration, data and custom code.
Do not leave an unsupported module in place merely because it has not caused a visible incident. The absence of a maintained release removes the normal destination for the next update. Add unsupported-project removal to the website roadmap with a named owner, deadline and acceptance tests.
Define ownership before the next advisory batch
- Business owner: confirms journey criticality, downtime tolerance and customer or regulatory consequences.
- Technical owner: owns the dependency inventory, exposure assessment, update branch and release evidence.
- Content or marketing owner: tests editorial workflows, forms, campaigns and analytics that technical smoke tests can miss.
- Hosting or managed-service provider: confirms infrastructure, backup, log, deployment and incident responsibilities in writing.
- Security or risk lead: sets priority rules, escalation thresholds, evidence requirements and incident-response triggers.
Set service levels by exposure, not by the day of the week. An internet-facing authentication bypass with a known exploit should not wait for a monthly maintenance window. A configuration-specific issue in a disabled feature can follow a controlled planned release, provided the mitigation is verified and tracked.
For technical takeovers, require the outgoing or incoming provider to identify the live code repository, deployment process, Composer lock file, hosting access, update notification recipients, backup evidence and all unsupported extensions. Without those basics, advisory response becomes archaeology.
Make Drupal Maintenance Operational
Use one week to establish the minimum evidence and ownership needed for the next advisory.
Days 1–2
Confirm ownership, code and hosting access, deployed versions, enabled projects, security coverage and current backups.
Days 3–5
Run update and dependency checks, triage open advisories, remove stale access and rehearse one update in staging.
Days 6–7
Agree priority rules, business-journey tests, release evidence, monitoring, rollback and the next maintenance date.
Drupal Security Advisory FAQ
Practical answers for business owners, digital teams and technology decision-makers.
Sources Checked
- Drupal Association: 256 Advisories in Five Months
- Drupal Security Team: security advisories
- Drupal Security Team: security risk levels defined
- Drupal.org: updating modules and themes using Composer
- Drupal.org: updating Drupal core via Composer
- Drupal.org: Update Status module overview
- Drupal.org: contributed-project security coverage
- Drupal.org: securing your site
- Australian Cyber Security Centre: defending medium businesses against AI-enabled attacks
- Australian Cyber Security Centre: small business cyber security handbook
Sources and product guidance were checked on 1 November 2026. Security advisories and fixed versions can change quickly; confirm the current advisory and project release pages before acting.
Turn advisory noise into a controlled maintenance plan
VaniTech can assess your Drupal inventory, prioritise real exposure, repair the update pipeline and provide ongoing security-focused support.