Drupal Webform Security Update: Patch 22 Flaws Now
Patch Drupal Webform 6.2.12 or 6.3.1, test forms and integrations, review evidence of misuse, and protect customer data with this practical response guide.
Drupal released Webform 6.2.12 and 6.3.1 on 23 September 2026 with a coordinated set of 22 security fixes and one additional hardening change. One advisory, CVE-2026-96355, is rated critical and can lead to information disclosure, stored cross-site scripting or remote code execution when a vulnerable form uses particular custom formatting.
This deserves immediate attention because Webform is not a niche add-on. Drupal.org reports more than 331,000 sites using the module. Organisations use it for contact forms, enquiries, applications, registrations, uploads, surveys and operational workflows—often with personal information moving into email, CRM, helpdesk, payment or reporting systems.
The correct response is broader than clicking update. Confirm every installation and branch, preserve evidence, create a restorable backup, deploy through a controlled environment, test the business journey around each form, and assess whether an exposed site shows signs of compromise. The Drupal Security Team also said this coordinated release was not covered by Drupal Steward, so site owners should not assume an external service has already mitigated it.
Why this update needs a controlled response
coordinated security fixes in each supported release
22
sites reporting Webform use on Drupal.org when checked
331,609
Drupal security risk score for the critical RCE advisory
18/25
fixed branches: 6.2.12 and 6.3.1
2
The risk is not limited to one form setting
The release notes group the fixes across four operational areas that teams should include in testing and review.
Submission access
Fixes strengthen access controls around submissions, JSON:API responses, exports, imports and temporary export files.
Handlers and integrations
Remote Post handlers, response tokens and connected services need regression testing after the module update.
Rendering and files
The release addresses unsafe rendering, uploaded-file delivery, configurable attributes, Entity Print and custom token or template formatting.
Availability and abuse
Resource-exhaustion protection, file-reference validation and Webform Share anti-spam handling are also part of the coordinated update.
First, identify every affected site and version
Do not start with the most visible production website and assume the job is complete. Search the full estate: public websites, campaign sites, intranets, portals, development environments, disaster-recovery copies and older domains that still resolve. Include sites run by agencies or hosting partners.
For each site, record the Drupal version, Webform branch, installed version, hosting owner, code repository, deployment method and whether the site accepts public submissions. Supported targets are:
- Webform 6.2.x: update to 6.2.12. The release page lists compatibility with Drupal 10.2.
- Webform 6.3.x: update to 6.3.1. The release page lists compatibility with Drupal 10.3 and Drupal 11.
Drupal.org says no other Webform versions are supported. If a site is on an older branch, treat that as a separate upgrade and risk decision rather than assuming the 23 September patch can be applied directly.
Map exposure by feature, not only version
Every supported site below the fixed version should be updated, even if a quick configuration review suggests the critical path is absent. Exposure differs across the 22 issues. Inventory file uploads, public and private forms, Webform Share, JSON:API, Entity Print, Remote Post handlers, exports, imports, custom attributes, tokens, multiple-value item formats and any custom modules that render or transform submission data.
Understand the critical remote-code-execution condition
CVE-2026-96355 concerns certain format templates being included in token replacement. The official advisory says an attacker may be able to submit data that is later evaluated as template code when the submission is rendered. Depending on configuration and other enabled modules, the result can range from information disclosure and stored cross-site scripting to remote code execution.
The critical path is mitigated when the affected site does not use a custom multiple-value item format containing submission-value tokens. That qualification helps incident triage, but it is not a reason to delay the update. The same release addresses many other access-control, rendering, file and denial-of-service issues, some of which concern publicly accessible forms or common integrations.
Separate two questions:
- Are we vulnerable? Confirm package version and relevant configuration.
- Was the vulnerability used? Review logs, files, accounts, configuration changes and downstream activity. A successful patch answers the first question only.
Move from inventory to verified recovery
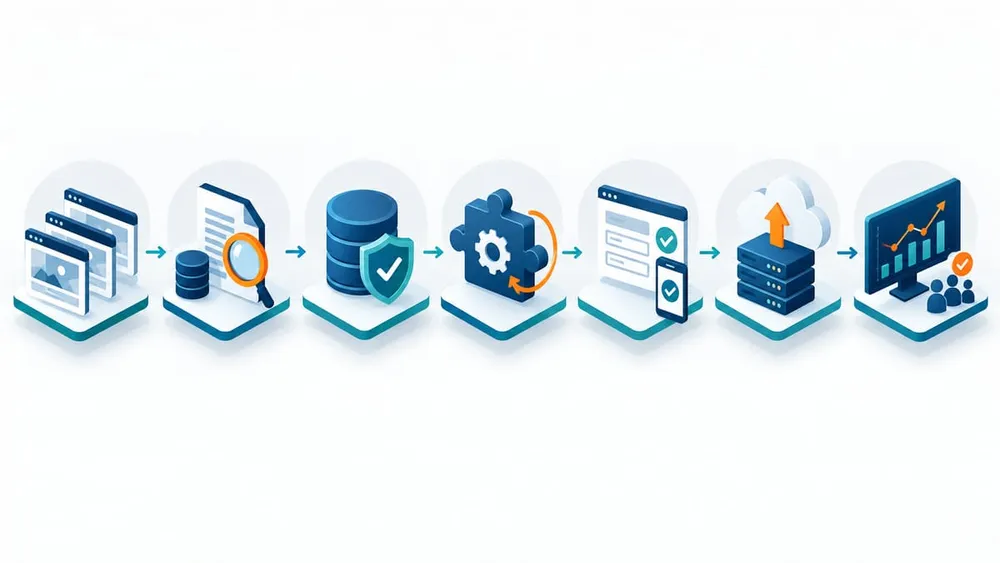
A seven-step Webform patch plan
- Open an incident or change record. Name the business owner, technical owner, affected sites, decision log and communication route.
- Preserve evidence before changing production. Retain relevant web, PHP, Drupal, WAF, authentication, file, database and integration logs according to your response plan. Record the current package and configuration state.
- Create and verify a restorable backup. Back up code, Composer files, database, private files, public uploads and environment-specific configuration. Confirm who can restore it and where restoration will occur.
- Update through Composer in a controlled environment. For a minor module update, Drupal's guide uses
composer update drupal/webform --with-all-dependencies, followed by database updates and a cache rebuild. Review the resulting dependency and lock-file changes. - Run technical and business tests. Test each high-value form, access path, upload, email, integration and export with representative roles and data.
- Deploy using the normal release path. Avoid editing package files directly on the server. Apply database updates, rebuild caches and verify configuration consistently across every instance.
- Monitor and reconcile. Check errors, submission volumes, emails, queues, CRM records, uploads and user reports. Compare the business outcome—not just the HTTP status—with a known-good baseline.
If dependency constraints prevent the fixed version from resolving, do not force an unreviewed production change. Identify the blocker, involve the maintainer or development partner, restrict affected capabilities where practical, and plan an expedited compatible deployment.
Test the complete form journey
A green homepage check does not prove that submissions, files, integrations and restricted data still behave correctly.
Anonymous visitors
Submit public forms, trigger validation, exercise multi-step flows, confirm spam controls and verify that restricted results remain unavailable.
Authenticated roles
Test least-privileged editors, reviewers and administrators against form building, submission access, imports, exports and handler configuration.
Files and rendering
Upload permitted and rejected files, retrieve authorised downloads, render emails or PDFs, and inspect custom tokens and multiple-value formatting.
Connected systems
Confirm Remote Post, CRM, helpdesk, email, queues, JSON:API consumers and analytics receive one accurate record without duplication or data loss.
Review for compromise instead of assuming patching closes the incident
The advisory describes possible information disclosure, stored cross-site scripting and remote code execution for the critical condition. If the affected configuration existed on an internet-facing site, review evidence proportionately. Useful questions include:
- Were unusual submissions or payload patterns received before the patch?
- Did PHP, the web server or the operating system launch unexpected processes?
- Did executable, template or unfamiliar files appear in writable directories?
- Were administrator accounts, permissions, handlers, email destinations or integration endpoints changed?
- Did exports, JSON:API responses, temporary files or private uploads show unusual access?
- Did downstream systems receive unexpected records, requests or authentication failures?
Absence of one log signal is not proof of safety. Retention may be short, proxies may hide client details, and successful misuse may leave evidence across several systems. Escalate to specialist incident response when the exposure, data sensitivity or available evidence exceeds the team's capability.
Protect the data behind the form
Forms often hold more risk than their simple front-end appearance suggests. A single workflow may collect identity details, health information, resumes, financial documents, support evidence or information about children and vulnerable people. It may then copy that data into email, a CRM, shared storage and reporting platforms.
If evidence suggests unauthorised access or disclosure, follow the organisation's incident and privacy response process. The OAIC's quick reference guide frames the response as four steps: contain, assess, notify when required, and review. It also notes that organisations covered by the Notifiable Data Breaches scheme must assess suspected eligible breaches and may need to notify affected individuals and the OAIC.
This article is technical guidance, not legal advice. Involve the appropriate privacy, legal, insurance and executive contacts when personal information may have been compromised.
If immediate patching is blocked
A temporary control should reduce exposure while the fixed release is prepared; it should not become a substitute for updating. Depending on the affected features and business need, teams may consider pausing a non-essential form, restricting access, removing risky custom formatting, disabling an exposed integration, tightening WAF monitoring, or directing users to a safe alternative channel.
Choose controls from the actual configuration and the official advisories. Avoid broad changes that destroy evidence or create a second outage. Document the owner, start time, customer impact, monitoring signal and expiry condition for every temporary measure.
Australian Signals Directorate guidance recommends patching in a timeframe appropriate to exposure and maintaining clear patch processes, defined responsibilities and vulnerability scanning. For an internet-facing module with a public critical advisory, the business case for delay should be explicit, short-lived and reviewed by an accountable owner.
Turn the emergency patch into a repeatable control
Four records make the next advisory faster to handle and easier to verify.
Software register
Track site, owner, Drupal version, Webform branch, hosting, repository, deployment method and support status.
Form inventory
Record purpose, data classification, uploads, handlers, integrations, retention, notification recipients and test owner.
Patch evidence
Keep the advisory, approved change, backup result, dependency diff, automated checks, manual test evidence and production verification.
Response ownership
Name who monitors advisories, approves urgent maintenance, investigates compromise and makes privacy or customer communication decisions.
A practical checklist for business owners
- Ask your website provider for the installed Webform version on every Drupal site.
- Confirm 6.2.x sites are moving to 6.2.12 and 6.3.x sites to 6.3.1.
- Request evidence of a current, restorable backup before production deployment.
- Identify forms that accept uploads or sensitive personal information.
- List systems that receive form data, including email, CRM, helpdesk and storage.
- Approve a short test plan covering anonymous, authenticated and administrative roles.
- Ask whether the risky custom-formatting condition existed and what compromise checks were performed.
- Confirm monitoring after release covers both technical errors and missing business records.
- Record who owns future Drupal and contributed-module security advisories.
A useful completion statement is specific: every known site is inventoried, every supported installation is on a fixed release, critical journeys have passed, evidence review is documented, and any privacy assessment has an accountable owner.
Sources checked
VaniTech checked the following primary and authoritative sources on 24 September 2026:
- Drupal Security Team public service announcements
- Webform 6.2.12 release
- Webform 6.3.1 release
- SA-CONTRIB-2026-175: critical remote code execution
- Drupal Webform project and support information
- Drupal guide to updating modules with Composer
- Australian Signals Directorate patching guidance
- OAIC quick reference guide for responding to data breaches