Shopify App IP Allowlist: November 2026 Guide
A practical guide to Shopify's November 2026 IP allowlist deadlines, testing steps, serverless ASN risks, merchant checks and app security controls.
Shopify announced on 5 November 2026 that IP allowlists are now required for public apps that call the GraphQL Admin API or REST Admin API. The first enforcement date is close: from 12 November, bulk queries and mutations can be blocked when an app has no allowlist. From 20 November, the app can be delisted, blocked from new installs and flagged to merchants in Shopify admin.
This is not only a developer compliance task. Public apps often sit inside product syncs, fulfilment, inventory, reporting, loyalty, CRM, ERP and customer-service workflows. A rushed network rule can interrupt those processes; doing nothing can create a visible supplier-risk warning and later API failure.
The practical response is to identify the app, map every place it sends Shopify API traffic from, choose the narrowest workable rule, test recent traffic, enable enforcement, and verify real business journeys. Merchants should also check whether their critical vendors are ready rather than assuming every installed app will meet the deadline.
A New Security Requirement With Immediate Commercial Deadlines
Shopify is moving IP allowlisting from recommended hardening to enforced public-app hygiene.
12 November
Bulk queries and mutations can be blocked for public apps without an allowlist.
20 November
Non-compliant apps can be delisted, blocked from new installs and flagged to merchants.
15 January
Merchants using an affected app are scheduled to see an admin warning.
1 April 2027
Shopify is scheduled to reject affected GraphQL and REST Admin API requests.
Public apps
The requirement applies to public apps calling the Admin API; custom apps are strongly recommended but not required.
Peak trading
The change arrives while many merchants depend most heavily on reliable integrations and bulk operations.
Know the enforcement sequence
| Date | Shopify action | Business implication |
|---|---|---|
| 12 November 2026 | Bulk queries and mutations from non-compliant public apps are blocked | Exports, catalogue jobs, reporting and high-volume syncs may fail first |
| 20 November 2026 | App can be delisted, blocked from new installs and flagged in Settings > Apps | Growth, merchant trust and vendor reviews are affected |
| 15 January 2027 | Merchants using the app see an admin warning | Support demand and supplier-risk escalation are likely |
| 1 April 2027 | Affected GraphQL and REST Admin API requests are rejected | Existing installations can lose core integration functions |
Existing installs do not all stop on 20 November, but that is not a reason to defer. The earlier bulk-operation block can already damage live workflows, and the merchant-facing flag creates an immediate commercial signal. Treat 20 November as a production-readiness deadline, not a paperwork date.
Separate merchant actions from app-owner actions
App owners and implementation partners control the Dev Dashboard setting, hosting architecture, outbound addresses, release process and API verification. They need to prove the allowlist covers production traffic without opening an unnecessarily broad network range.
Merchants normally cannot configure a third-party public app's allowlist. They can still inventory critical apps, review Shopify's app-security indicators, ask vendors for a remediation date, identify which workflows use bulk operations and plan a continuity option.
Internal custom-app teams are outside the mandatory public-app rule, but the same control may be worthwhile. Shopify strongly recommends allowlisting custom apps because a stolen Admin API token is otherwise usable from any network until another control stops it.
Write down who owns each decision. A merchant waiting for a vendor and a vendor waiting for a hosting provider can both believe somebody else is handling the deadline.
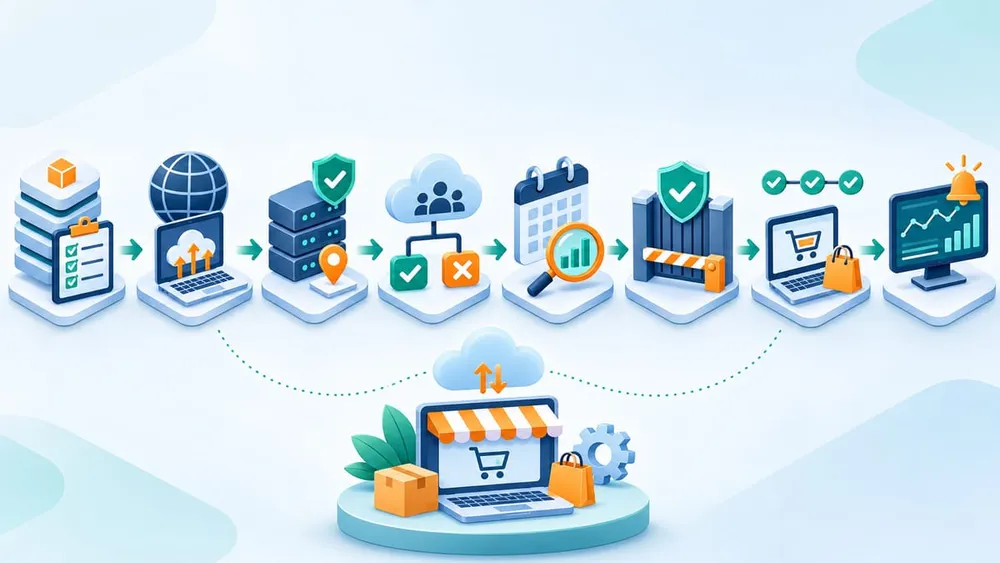
Use an eight-stage path from traffic inventory to monitored enforcement
A safe rollout starts with evidence, not guesses. Map where the app really calls Shopify from, classify static and dynamic egress, account for jobs and failover paths, test Shopify's view of recent traffic, enable the smallest rule set and verify business outcomes.
The goal is not merely to make the dashboard show compliant. It is to constrain stolen-token use while keeping legitimate API traffic observable and supportable.
1. Confirm the app and API scope
Confirm whether the app is public or custom, whether it calls GraphQL Admin API, REST Admin API or both, and whether it used a bulk query or mutation in the previous 180 days. List production, staging, worker, scheduler, webhook-handler, queue and support-tool codebases that can make those calls.
2. Inventory every outbound path
Record the public egress address for each runtime, region, background worker and disaster-recovery path. Look beyond the web process: scheduled catalogue jobs, fulfilment consumers, data exports and one-off support tools often run elsewhere.
Use infrastructure records and API logs rather than asking a developer to remember the architecture. Include IPv6 if the runtime can reach Shopify over it, and document any NAT gateway or egress proxy that changes the address Shopify sees.
3. Choose static IPs before shared networks
Shopify supports IP addresses and CIDR ranges for static egress. This is the narrower option because the rule identifies your own public addresses. Use the smallest valid ranges and remove environments that no longer call the Admin API.
4. Use ASN rules carefully for serverless hosting
Dynamic outbound addresses are common on serverless platforms. Shopify supports allowlisting a provider network by autonomous system number, with optional country restrictions. The trade-off is wider trust: other customers share that network, so a stolen token used from the same allowed ASN may pass the network check.
Prefer dedicated egress, NAT or a proxy with stable addresses when the platform and budget support it. If ASN rules are necessary, allow only the required networks and countries, document why they are needed and schedule a later architecture review.
5. Test the previous 30 days of traffic
Use Test against recent traffic in the Dev Dashboard before enforcement. Shopify checks whether any API source observed during the previous 30 days would be blocked. Investigate every unexpected address instead of blindly adding it; it could be an old environment, a forgotten job or suspicious activity.
6. Enable enforcement and prove the boundary
Save the rule, turn on enforcement and verify both sides: legitimate production requests succeed, while a controlled request from outside the allowlist fails with HTTP 403. Store the test result, rule owner, change date and rollback conditions with the release record.
7. Test business journeys, not only API health
A successful product query proves little about a fulfilment or refund workflow. Exercise representative journeys across the systems that depend on the app.
| Scenario | Expected evidence | Failure to watch |
|---|---|---|
| Bulk catalogue export | Job completes with expected record count and duration | Blocked bulk operation, partial data or silent retry loop |
| Order-created webhook follow-up | Handler receives event and authorised Admin API lookup succeeds | Webhook succeeds but background lookup returns 403 |
| Scheduled inventory sync | Every worker region can read and update intended stock records | One region or failover worker is missing from the rule |
| Merchant admin workflow | Interactive app actions work with the right staff permissions | Network fix hides a separate authentication or scope problem |
| Disaster-recovery path | Standby environment has a documented, tested egress rule | Failover starts but API access is blocked |
| Outside-network probe | Known test request receives 403 | Rule is not enforced or is broader than intended |
8. Monitor and review after release
Review API logs for unexpected addresses, watch 401 and 403 rates, alert on failed bulk jobs and re-test after hosting, region, network or worker changes. ASD guidance supports central logging for API activity that changes or exposes non-public data. Keep enough evidence to connect a merchant incident to the source runtime, token, app version and downstream job.
Check Shopify's compatibility boundaries before enforcing
Shopify documents two important patterns that do not work with the allowlist because it cannot confirm their source address: access tokens used by Shopify Flow's Send HTTP request action and Admin API requests made directly from an Oxygen-hosted storefront.
Do not solve those cases by widening the rule. Move the Admin API call behind a controlled app backend, redesign the token flow, or use a supported direct-access pattern. Shopify also documents request types that are never rejected by the allowlist, including development-preview requests on dev stores and direct API access from embedded app pages or POS UI extensions.
This boundary is why a route-level inventory matters. An application can appear to work during an interactive admin test while a background or storefront-origin request fails later.
Do not treat allowlisting as complete app security
An IP rule limits where a token can be used; it does not reduce what the token can access, detect every leak or repair an insecure endpoint. Pair it with the rest of Shopify's current security model:
- migrate public apps to expiring offline access tokens before the separate 1 January 2027 deadline;
- request only the Admin API scopes the app uses;
- keep client secrets and private keys out of source code, browser bundles and logs;
- rotate credentials regularly and immediately after suspected exposure;
- authenticate webhooks, app proxies and interactive requests;
- scope stored records to the authenticated shop;
- run Shopify app security checks on every release and scan separate backends or internal tools;
- review API logs and maintain an incident-response owner.
Shopify's expiring offline tokens last one hour, while allowlisting constrains the networks from which that token works. These controls reduce different parts of the same credential risk and are stronger together.
Questions to Answer Before You Turn On Enforcement
Use these prompts with app, cloud, integration, support and merchant stakeholders.
Ownership
Who owns the app, hosting account, Dev Dashboard setting and deadline sign-off?
Traffic
Which production, worker, scheduler, webhook and recovery paths call the Admin API?
Egress
Are outbound addresses static, behind NAT, dynamic or shared through an ASN?
Bulk work
Which catalogue, order, inventory or reporting jobs depend on bulk operations?
Compatibility
Does any token originate from Flow HTTP actions, Oxygen or another unconfirmable path?
Testing
Do recent-traffic results cover peak, month-end and failover workloads?
Boundary
Has an outside-network request been confirmed to fail with HTTP 403?
Monitoring
Who receives alerts for API 403s, failed bulk jobs and unexpected source addresses?
Merchant plan
What will merchants do if a critical vendor misses the deadline?
A practical seven-day response plan
Day 1: inventory and assign
Confirm public-app status, business owner, technical owner, hosting owner, Admin API use and bulk-operation exposure. Merchants should list their critical third-party apps and contact vendors with unclear status.
Day 2: map network paths
Collect public egress evidence for every runtime, region, worker, scheduler and recovery path. Identify dynamic or unsupported origins before making a rule.
Day 3: design the narrowest rule
Prefer static addresses and constrained CIDR ranges. Where an ASN is unavoidable, document the shared-network risk and restrict countries.
Day 4: test recent traffic
Run Shopify's 30-day test, reconcile every observed source and investigate unknown addresses. Add only legitimate dependencies.
Day 5: enforce and verify
Enable enforcement in a controlled release. Test interactive, webhook, scheduled, bulk and failover journeys, then prove an outside request receives 403.
Day 6: monitor and communicate
Watch API errors and job outcomes, brief support teams and give merchants a concise confirmation of scope, test evidence and residual risks.
Day 7: close the next security gap
Schedule expiring-token migration, scope review, credential rotation and CI security checks. Add network-change review to the app's deployment and hosting processes.
Shopify IP Allowlist FAQs
Practical answers for merchants, app owners and integration teams.
Sources checked
- Shopify: App security updates — IP allowlist is now required
- Shopify Developer Documentation: Restrict API access with an IP allowlist
- Shopify Developer Documentation: About app security
- Shopify Developer Documentation: Use expiring offline access tokens
- Shopify Developer Documentation: Run app security checks in CI/CD
- Shopify Developer Documentation: Manage app credentials
- Australian Signals Directorate: Information Security Manual — web APIs
Sources were accessed on 10 November 2026. Shopify requirements and dates can change; verify current documentation and the Dev Dashboard before implementation.
Need Help Securing a Shopify App or Integration?
VaniTech can map your Shopify API traffic, review hosting and token architecture, configure controlled egress, test business workflows and build ongoing monitoring before enforcement interrupts operations.