WordPress 7.1.1 Security Update: Patch Guide
Patch WordPress 7.1.1 safely with a practical backup, staging, regression-testing, rollback and post-update monitoring checklist for business websites.
WordPress released version 7.1.1 on 17 September 2026 and recommends that sites update immediately. The release contains 11 security fixes, 17 Core bug fixes and 19 Block Editor fixes. The security list includes stored cross-site scripting paths, a specially crafted URL that can install and preview an inactive theme, authenticated path traversal in the REST Templates Controller, arbitrary post overwrite by Contributor-level users and several authorisation or information-disclosure issues.
For a business website, the correct response is not simply to click Update and move on. The release changes both security-sensitive and editor-facing behaviour, so the operational goal is to reduce exposure quickly while proving that the public site, administration area, publishing workflows and revenue-critical journeys still work.
This article separates confirmed WordPress facts from VaniTech's recommended implementation process. WordPress has not stated in the release notice that these issues are being actively exploited, so avoid turning the advisory into an unsupported breach claim.
What changed in WordPress 7.1.1
The patch covers multiple attack surfaces as well as Core and Block Editor defects, so both security and regression testing matter.
11 security fixes
The official list includes XSS, path traversal, authorisation, content-integrity and information-disclosure issues.
17 Core fixes
Maintenance changes affect the platform beneath themes, plugins, custom code and integrations.
19 Block Editor fixes
Marketing and content teams should test editing, previewing, reusable content and publishing workflows.
Immediate update advice
WordPress explicitly recommends updating sites immediately and says automatic background updates will begin on eligible sites.
Who should act now?
Start with every production WordPress site that your organisation owns, funds or relies on—not only the main marketing website. Include campaign sites, microsites, portals, franchise sites, old subdomains, staging systems reachable from the internet and installations maintained by another agency or hosting provider.
WordPress 7.1.1 is the current release. The security fixes are being backported where necessary to branches eligible for security fixes, currently through 4.7, but the release notice says those backports are still in progress and reminds users that only the newest WordPress version is actively supported. If a site cannot move directly to 7.1.1, confirm the exact backported version for its branch rather than assuming that an older version is covered.
Assign one owner for the change. That person should know where the site is hosted, how it is backed up, who can approve a rollback, which plugins and themes are business-critical, and which journeys must be tested after deployment.
Inventory before you patch
Create a short register for each site: current WordPress version, PHP version, active theme and child theme, active and must-use plugins, hosting platform, CDN or web application firewall, cache layers, scheduled jobs, payment or booking integrations, forms, SMTP provider, analytics and consent tooling, and the current administrators and editors.
Also record whether WordPress Core automatic updates are enabled. WordPress enables minor Core updates by default on existing installations; new installations created on WordPress 5.6 or later normally receive both minor and major Core updates unless WordPress detects a version-control checkout. Configuration constants, filters, managed-host settings and deployment pipelines can change that behaviour.
This inventory turns a generic patch into a controlled change. It also prevents a common support failure: discovering after the update that nobody knows who owns the CDN cache, the licence for a premium plugin or the credentials for the deployment system.
Move from exposure to verified operation
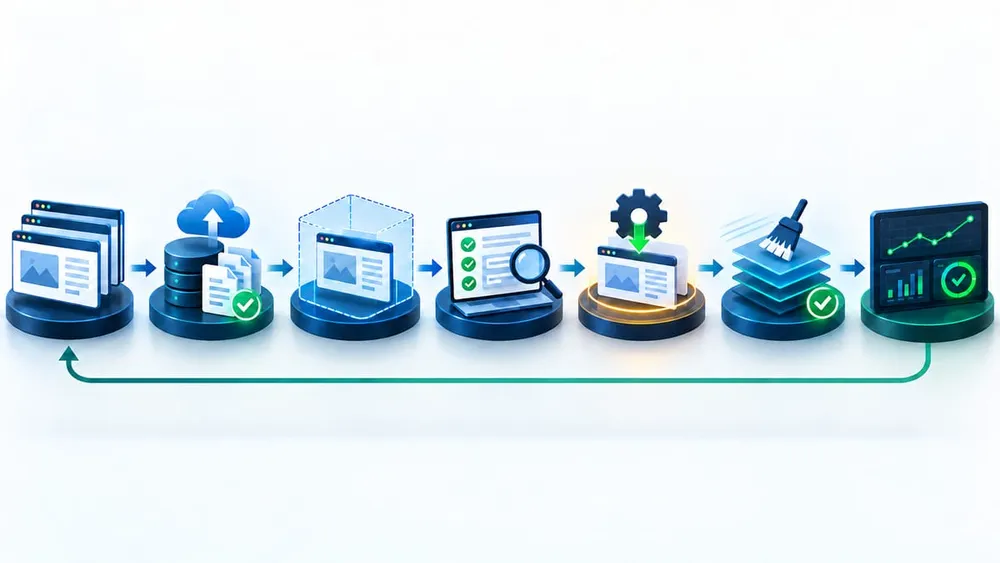
A seven-step WordPress 7.1.1 patch plan
Move quickly, but keep enough evidence to know what changed and recover if a dependency fails.
1. Confirm versions
Record Core, PHP, theme and plugin versions plus the owner of each production site.
2. Back up and prove access
Capture database and files, then confirm the backup is readable and the restore credentials are available.
3. Rehearse safely
Clone production to staging or another private test environment and apply the same update there first.
4. Run targeted tests
Exercise public pages, admin login, Block Editor, forms, search, ecommerce, integrations and scheduled tasks.
5. Deploy attended
Patch production during an owned window with monitoring open and a tested rollback decision.
6. Purge and verify
Clear WordPress, server and CDN caches, then test as an anonymous visitor and as each important user role.
7. Monitor and close
Watch errors, security alerts, conversions and editor reports, then record evidence and remaining actions.
Back up for restoration, not reassurance
WordPress's update documentation recommends backing up before an update so the site can be restored if something goes wrong. For a useful recovery point, capture both the database and the files needed to reconstruct the installation, including wp-content, configuration, custom plugins, custom themes and deployment-specific files.
Do not treat a green backup job as proof of recoverability. Confirm the timestamp, storage location, retention, encryption where appropriate, and the person who can restore it. For a critical site, perform a test restore into an isolated environment or at least verify that the archive opens, the database export parses and the documented restoration path still matches the hosting platform.
Record a rollback trigger before production deployment—for example, a fatal error, failed checkout, broken authentication, repeated payment callback failures or an editor-blocking regression that cannot be contained quickly.
Test the journeys the business depends on
| Area | What to test | Evidence to keep |
|---|---|---|
| Public website | Home, service and campaign pages; navigation; responsive layouts; media; search; redirects; 404 pages | Key URLs, screenshots where useful, browser console and server-error review |
| Content operations | Admin login; create, edit, preview, schedule and publish; media upload; revisions; reusable or synchronised content | Test content ID, roles used, publish result and any editor warnings |
| Lead generation | Contact, quote, newsletter and gated-download forms; validation; spam controls; email and CRM delivery | Submission ID and confirmation in every downstream destination |
| Ecommerce or bookings | Browse, search, cart, coupon, checkout, payment, confirmation, refund or cancellation and stock or booking updates | Test order or booking IDs plus payment and fulfilment records |
| Integrations | Webhooks, REST endpoints, scheduled imports and exports, analytics, consent signals and single sign-on | Request IDs, job status, destination records and error logs |
| Operations | Cron, queue processing, cache purge, backups, uptime checks and security monitoring | Run timestamps, alert state and before-and-after error rates |
The official release contains 19 Block Editor fixes, so content-authoring checks are part of the patch—not optional polish. WordPress's theme testing guidance also recommends checking standard blocks, different devices, JavaScript errors and target browsers.
Automatic updates still need operational ownership
An eligible site may already have received WordPress 7.1.1 automatically. That reduces the exposure window, but it does not complete the operational work. Confirm the installed version from a trusted administrative view or deployment record, review the update notification, run the same critical-journey tests and investigate any new errors.
Do not disable automatic security updates as a reflex. WordPress says automatic minor updates are a deliberate security default and strongly discourages disabling them. Instead, make the surrounding system safer: dependable pre-update backups, an external uptime check, error reporting, an owned administrator email address, a support contact and a short post-update test pack.
If a managed host applies Core patches, clarify the boundary. Ask whether the host tests plugins, themes, custom code, checkout, forms, CRM delivery and CDN behaviour—or only confirms that WordPress Core updated successfully.
If the update fails
Keep the public status, deployment timeline and error logs together. WordPress documents Recovery Mode for fatal PHP errors during regular page loads: affected plugins or themes are paused for the administrator's recovery session so the operator can log in, identify the component and temporarily deactivate it. Recovery Mode is useful, but it is not a substitute for a known-good restore path.
After a failed update, decide whether the site is safe to keep online while you isolate the issue. A cosmetic defect may be containable; broken authentication, checkout, form delivery, access control or data integrity usually deserves rollback or maintenance-mode treatment. Preserve logs and the failed environment before replacing it if those records may help diagnosis.
WordPress also documents clearing a stuck .maintenance file after a failed manual update and completing any required database upgrade through the administration area. Use those steps only after confirming that the code and database versions are consistent and that a backup is available.
Patch first, then reduce the wider risk
WordPress Core is only one layer of the website. After the urgent update is stable, review active plugins and themes, remove abandoned or unnecessary components, check administrator and editor accounts, verify multifactor authentication where supported, restrict production file editing, confirm least-privilege access, and review the web application firewall and origin exposure.
Because several 7.1.1 fixes involve authenticated roles or content operations, inspect users with Contributor access or higher and remove accounts that no longer need access. Review recent content, theme installation activity and administrative changes against your normal audit trail. This is a precautionary control, not evidence that the site has been compromised.
WordPress's hardening guidance treats security as risk reduction and containment rather than a one-time state. A maintenance owner, asset register, backup test, update policy and incident contact are more valuable than a collection of security plugins that nobody monitors.
Monitor the first day and the first week
For the first 24 hours, watch HTTP 5xx responses, PHP fatal errors, login failures, form-delivery failures, payment or booking errors, background-job failures, unusual cache behaviour and external uptime checks. Compare against a normal baseline where one exists.
Over the next seven days, ask content and marketing teams about editor warnings, preview failures or publishing changes; reconcile leads, orders and bookings against downstream systems; confirm scheduled jobs ran; and review security and access logs for unexpected patterns.
Close the change only when the installed version is recorded, high-value journeys pass, caches are stable, no material error increase remains, the backup retention decision is documented and any deferred plugin, theme or infrastructure work has an owner and due date.
Questions to ask your developer, host or support partner
- Which of our WordPress sites are on 7.1.1, and how was that verified?
- If a site is on an older branch, which exact backport contains the relevant fixes?
- When was the last restorable database-and-files backup created and tested?
- Which plugins, themes, customisations and integrations were tested against the patch?
- Who owns the production rollback decision and how long would restoration take?
- Are Core automatic updates enabled, and where are success or failure notifications delivered?
- Which user roles and administrative accounts were reviewed after the security release?
- What will be monitored for 24 hours and reconciled over the following week?
Sources checked
- WordPress 7.1.1 Maintenance and Security Release
- WordPress: Updating WordPress
- WordPress Advanced Administration Handbook: Upgrading WordPress
- WordPress Advanced Administration Handbook: Hardening WordPress
- WordPress: Recovery Mode
- WordPress Theme Handbook: Testing
- WordPress Playground Handbook: Test
Sources were accessed on 18 September 2026. Product behaviour and backport status can change; verify the current release information before acting on an older WordPress branch.